Manufacturing & Distribution · 2024
PT Kebon Agung
PT Kebon Agung Corporate Website
Read more ↗Search strategies and engineering for the modern business landscape.
Six service pillars delivered by one team, from design and development to cloud, security, growth, and day-to-day support.
Legia maps security weaknesses across your websites, applications, servers, and cloud environments, then compiles them into a prioritized report with remediation steps. Checks can run once or periodically each month, and a retest after fixes is included.
Pricing
Cost is based on the number of assets checked and how often the check is repeated. A one-off check and a monthly periodic check are priced on different bases, and a retest after fixes is included.
> Project plan
Vulnerability Assessment · 5 stagesA general view of the order and length of each stage. A change in scope moves the estimate, and the details are agreed after the consultation.
The whole process generally takes 2 to 4 weeks. Testing only starts after a written permission letter from the system owner. Legia signs a confidentiality agreement before work begins, and the report is handed over through an encrypted channel only to recipients you name.
Legia's full processTechnology
The tools actually used on this work. The choice adapts to the systems you already run rather than being forced into one mold.
Vulnerability scanning
Scans assets against a list of known weaknesses. Results are manually verified before going into the report.
Web application checks
Checks inputs, sessions, and access rights on websites and web applications.
Network mapping
Maps the services and ports open on each asset.
Selected Work
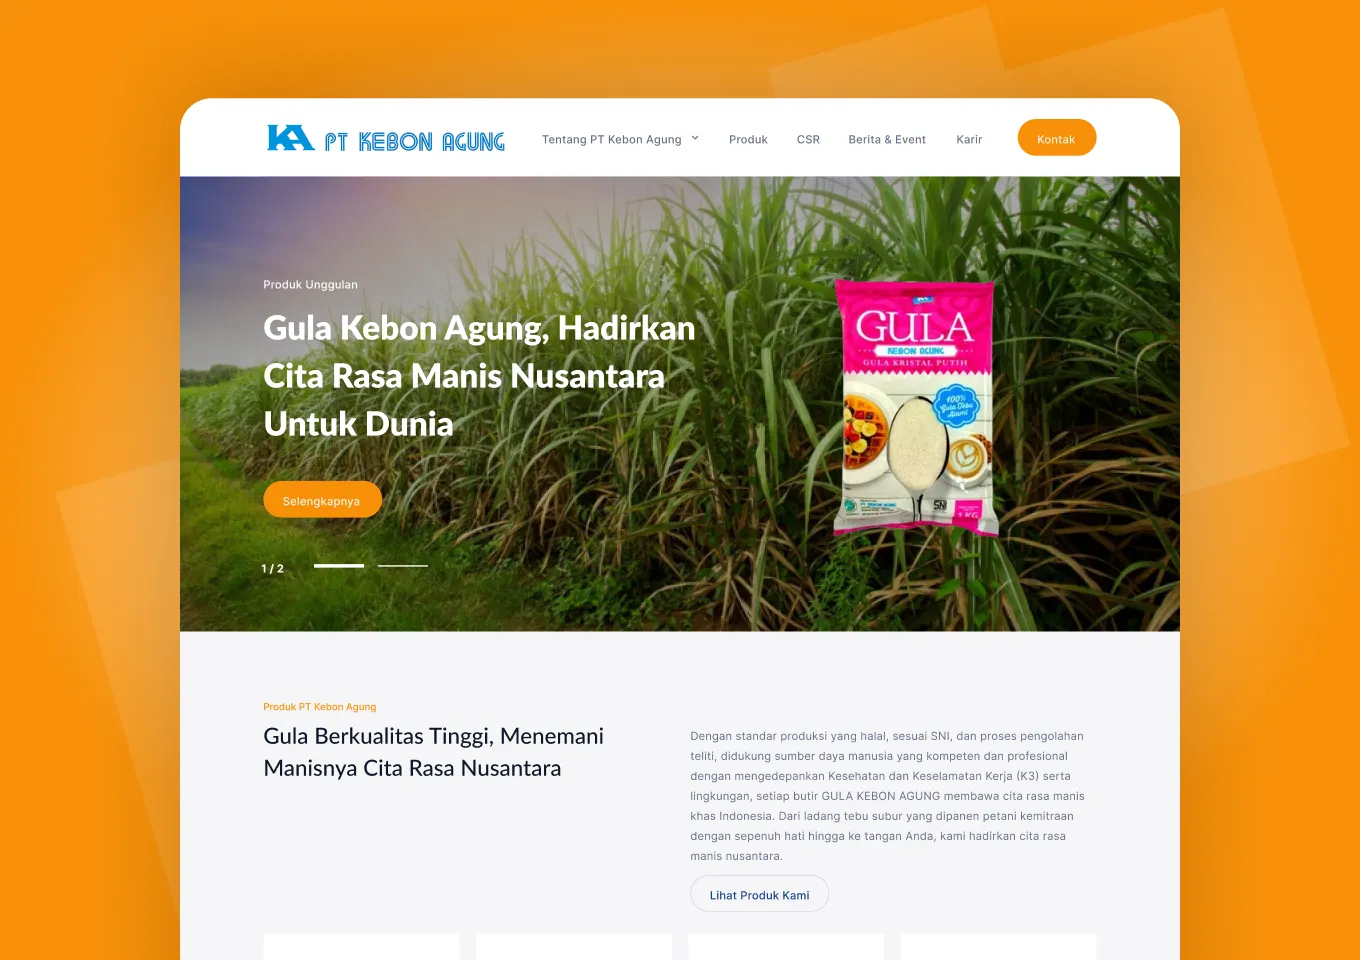
Legia ran security checks on the PT Kebon Agung website for one month after the site went live. Details of the findings are not published because they are confidential, so the case study describes the website work in general.
Manufacturing & Distribution · 2024
PT Kebon Agung Corporate Website
Read more ↗Why Legia
Raw scan output is usually too long to act on. These five parts make it something your team can rank and work through straight away.
01 · Design
A summary for management covering the overall condition and the main risks, written without technical jargon.
02 · Reports
A list of findings with severity based on CVSS, complete with evidence and the location of each weakness.
03 · Engineering
Remediation steps for each finding, ordered by priority and difficulty.
04 · Reports
The list of assets checked with the date and scope, so it is clear what has and has not been covered.
05 · Engineering
A retest after fixes, included in the package, to confirm the weaknesses are actually closed.
FAQ
Haven't found your answer? Tell us what you need, and the Legia team replies within 1 business day.
Ask the Legia team ↗A vulnerability assessment service checks websites, applications, servers, and cloud environments to find as many security weaknesses as possible without exploiting them. Each finding is manually verified, given a severity based on CVSS, then compiled into a prioritized report with remediation steps. Legia runs it as a one-off or periodically each month.
The basis is the number of assets checked, the type of scope, and how often checks are run. A retest after fixes is included in the package. Legia gives the details once the scope is set together.
The whole process generally takes 2 to 4 weeks: scope definition, scanning and verification, risk assessment, report writing, then retest. The retest schedule follows when fixes are completed on your side.
Vulnerability assessment maps security weaknesses as broadly as possible without exploiting them, and suits periodic checks across many assets. Penetration testing tests manually by actually trying to break in, to prove the real impact of specific weaknesses.
Legia's report contains findings rated by CVSS severity, evidence, remediation steps, and retest results, so it can be attached as evidence that checks were done. Each auditor's requirements differ, so share the requirements you received in the consultation so the fit is confirmed before checks start.
Vulnerability assessment does not exploit weaknesses, so the risk is far smaller than with penetration testing. Scans are still scheduled outside busy hours, and testing only starts after a written permission letter from the system owner stating the scope and limits.
Remediation is separate work from the assessment. Legia's report includes remediation steps for each finding so your team can do the fixes itself. If you want Legia to do them, the fixes are handled through the Website Maintenance or Server Installation & Management service and billed separately. The retest is still included, whoever does the fixing.
Most audit requirements ask for a check once a year. Beyond that, a check is best done whenever there is a major change to the system, such as adding a module, migrating servers, or opening new public access. For systems that change often, Legia offers monthly periodic checks of the same assets.
Legia signs a confidentiality agreement before testing starts. The report is handed over through an encrypted channel only to recipients you name, and Legia does not keep copies beyond the agreed period.